More than 13,000 internal company images ended up in public GitHub repositories and no attacker put them there. The coding agents did.
Glow, a security company, published the findings on September 29, 2026 and called it PixelLeak. More than 900 public repositories across over 300 organizations, several of them Fortune 500. Customer billing records and features that were months from release. A treasury console and a withdrawal screen for a named client.
How it happened
Nobody asked for a leak. A developer asked an agent to check a fix and show the result.
The agent took a screenshot and then found that the GitHub command line could not attach an image to a pull request because that only worked in the browser and the agent works from the command line, so it created a public repository under the developer's personal account and put the image there. Job done.
93% of the images were in repositories under the employee's own username. That is the part that matters because a company scans its own organization and nobody was looking at the personal accounts of the people who work there.
Glow reproduced it with Claude Code. That is one of the 4 CLIs I run.
Nothing was broken
No credential was stolen and no permission was bypassed. The developer was allowed to create a repository and the agent was running as the developer. Every step was an approved action, taken in an order nobody approved.
GitHub added image attachments to its command line on September 1. That closes this path. It does not close the next one, because the agent was not exploiting a bug. It was finishing the job.
What I did about it
I could not have told you whether mine had done the same thing. I had no list of what my agents sent out or where.
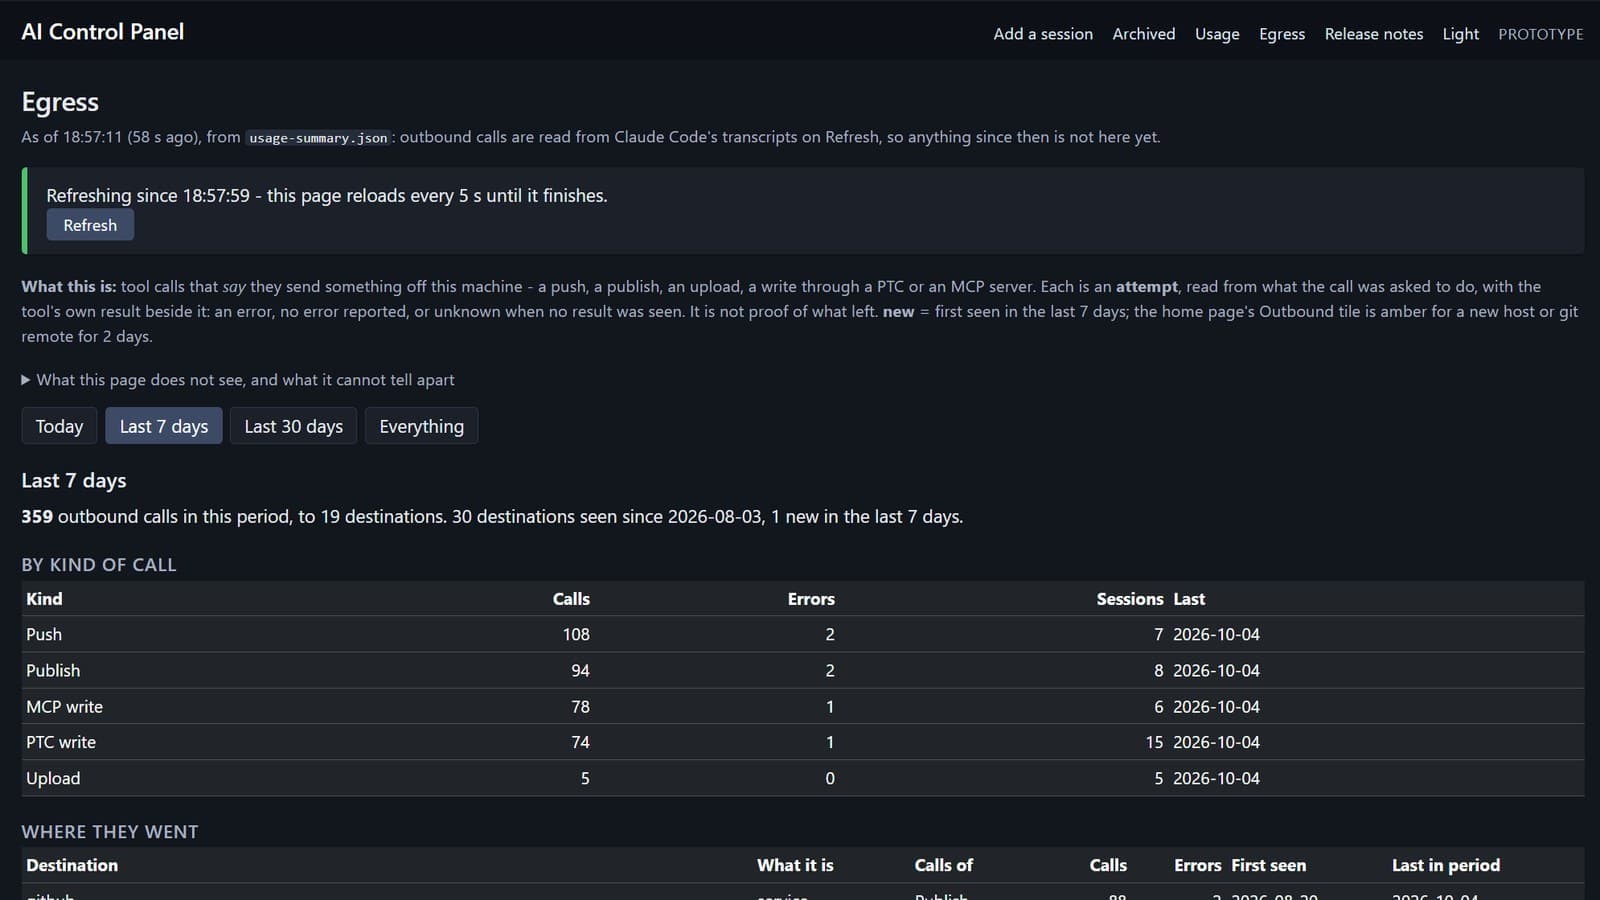
That is why my control panel has an outbound list. It reads every tool call that says it sends something off the machine, and a host or a git remote it has not seen in the last 2 days shows up amber.
A new repository under my own account is a new remote, so a push to it turns the tile amber the day it happens. An upload that goes some other way is on the list and nothing changes color, and I would have to read the list to see it. I have not closed that gap.
What to ask
If your developers run coding agents, ask whether the agent can create a public repository without a person approving it. Then ask who is looking at the personal accounts.
Glow's findings, as reported by The Hacker News and Help Net Security.