One change, three reviews, one green run
This is a real change to this website, replayed step by step. On 28 October I added the privacy policy you can read at /privacy. Before it shipped it went through the loop I run on code changes: a review in a separate session that did not write the code, fixes, a re-review, and an end-to-end test run against a preview of the site.
Nothing here is a mock-up. The findings, the line numbers and the test counts come from the review report and the test runs.
Step 1
The change
A privacy page has one job: say exactly what the site collects. This change added /privacy, a link to it in the footer of every page, a note under the contact form, and entries in the sitemap and llms.txt. It touched 9 files and added 140 lines.
Step 2
First review, commit 5e79a7f
The review read the policy against the code that handles the contact form. Most of it was true. 2 statements were not, and 2 left something out.
- Medium, page.tsx line 41. The page said we keep 3 campaign tags from the link you arrived on. The code keeps the whole address, so an ad click ID would be kept too, and sent to the database, the notification email and the task list.
- Medium, page.tsx line 47. The page promised the IP address was held for up to an hour. The rate limiter only clears an address when that same address posts again, so it can stay in memory for as long as the server stays warm.
- Low, page.tsx line 65. Vercel's own documentation lists 2 analytics data points the page did not: filtered link parameters and network speed.
- Low, page.tsx line 90. The deletion promise named 3 places. The code also writes the sender's email to the server logs when a message is caught as spam or every delivery fails.
Verdict: approved with comments. The 2 Mediums had to be fixed before it could ship.
Step 3
The fix
I fixed the wording, not the code. Each statement now says what the code does: the full first address with its tags, the IP kept only to limit repeat submissions, the 2 analytics data points, and the server logs named.
Step 4
Re-review, commit 4b0463c
All 4 findings closed. The re-review found one more. The paragraph about browser storage still described only campaign tags and left out the page that linked to us. It was a Low, but it was still untrue, so it got fixed.
Step 5
Final review, commit 016cf9b
Approved. 0 Critical, 0 High, 0 Medium and 0 Low open.
Step 6
The test run
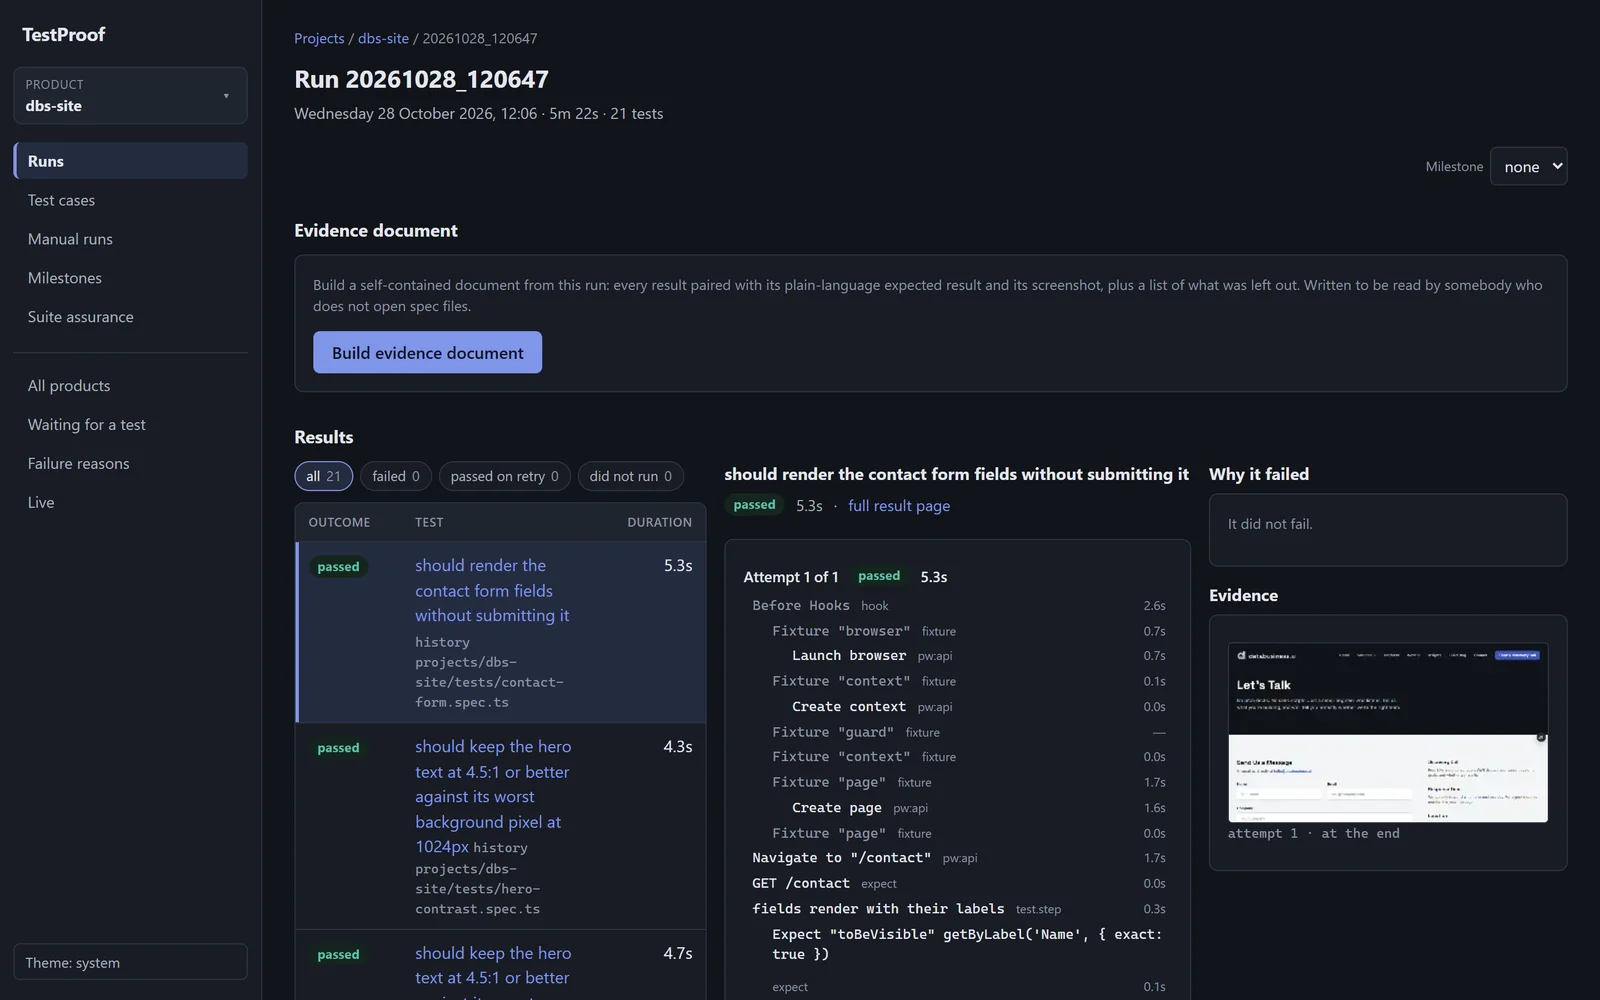
The end-to-end suite ran against a preview of the site at 016cf9b: 21 tests, 21 passed. 5 of them check the privacy page itself. It loads, the footer and the form link to it, the sitemap and llms.txt list it, and it does not scroll sideways on a phone.
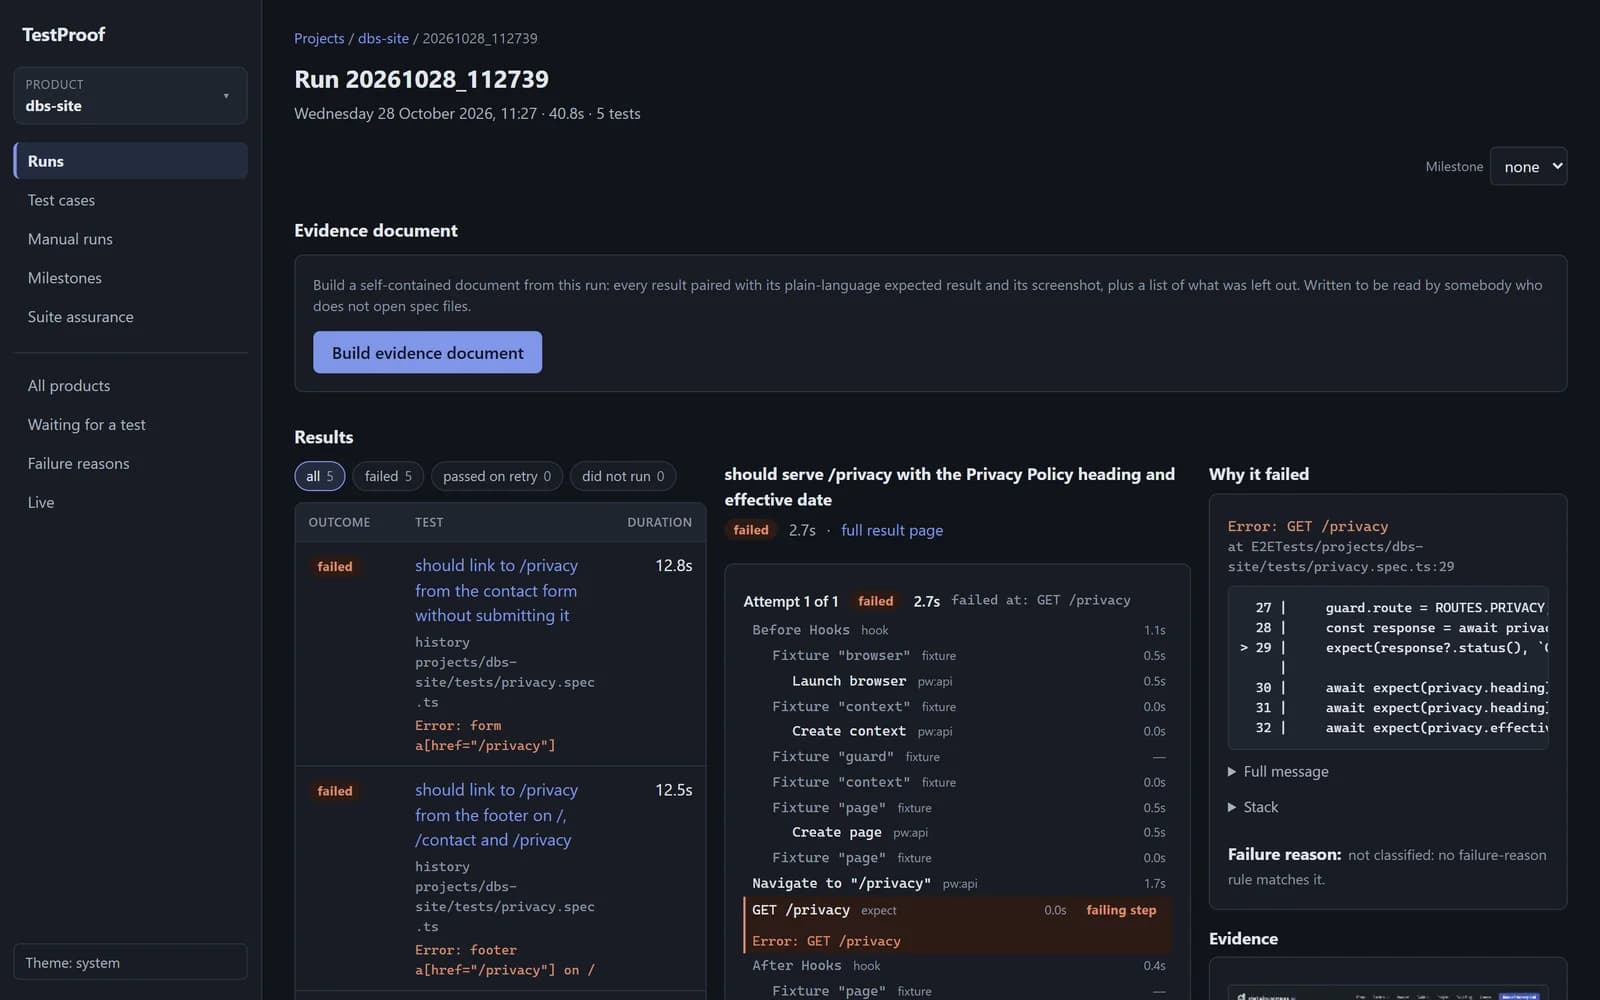
A green run only means something if the tests can fail. So the same 5 tests also ran against a preview from before the change. All 5 failed.
Step 7
Shipped
Merged as 7ba9302 on 29 October. The page at /privacy is that commit.
This is the review I sell. If you built something with AI and want to know what this would find in it, get in touch. How the loop works is on the code review page, and the tool that reads the test runs is on the TestProof page.